AI-driven cyberattacks: how can you strengthen your defences?
Artificial intelligence enables cybercriminals to launch attacks faster than ever. How can you spot the early signs of an intrusion and take action before your business suffers damage? Find out how to adapt your defences to this changing landscape.
Artificial intelligence (AI) and automation help cybercriminals identify security vulnerabilities, target victims and escalate attacks more easily and quickly, leaving you less time to respond.
Once inside a network, an attacker may seek to access other systems, steal confidential information and encrypt data. The longer these activities go undetected, the greater the damage can be.
There is no such thing as zero risk and preventive measures alone cannot guarantee complete protection. Your organization must therefore be prepared to detect intrusions quickly and take action to limit their impact.
How can an SOC help safeguard your business?
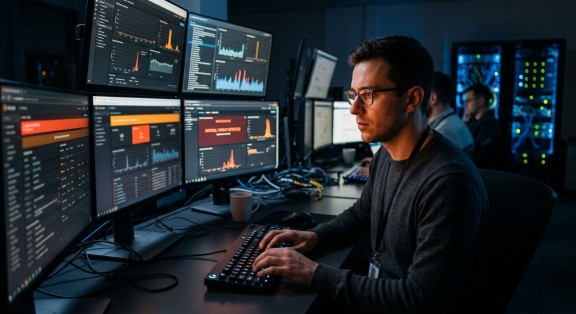
A Security Operations Centre (SOC) brings together technology and the expertise of security specialists to monitor IT environments, detect threats and coordinate responses.
Monitoring runs continuously, 24 hours a day, 7 days a week, to detect suspicious or unusual activity and enable incident response, even outside business hours.
However, an SOC does more than simply receive alerts. Its analysts review the vast amount of information generated by security systems to distinguish normal activity from suspicious or malicious behaviour.
How do AI and specialists complement each other?
SOCs have used artificial intelligence for several years to support the work of analysts. In response to increasingly common cyberattacks, AI helps in particular to:
- Analyze large volumes of data from networks, workstations and applications.
- Connect seemingly harmless events, which, when taken together, may point to the early stages of an intrusion.
- Prioritize alerts so analysts can focus on the most concerning situations.
- Speed up investigations by automating certain repetitive tasks, such as gathering information about an incident.
Let’s take the example of three low-severity alerts: an unusual log-in, a change in access rights or abnormal activity on a workstation. Each could have a legitimate explanation. However, analyzing them together may reveal the initial moves of a cybercriminal.
This is where an analyst’s judgment and experience come into play. They must determine whether these events actually constitute malicious activity, assess the severity of the situation and decide on the appropriate course of action.
Some actions can be automated within a clearly defined framework. Others require human approval, especially where they could interfere with your business operations. Isolating a device or blocking an account may help contain an attack, but a wrong decision could also disrupt essential activities.
A fully automated SOC is therefore not the best solution. Effective defence balances technologies that speed up detection and response with specialists who provide the human oversight needed to assess situations and make sound decisions.
Does your organization have the resources to respond in time?
Ask yourself these three questions to assess your organization’s response capabilities:
- Are your systems monitored around the clock? Suspicious activity must be addressed even when internal teams are out of the office.
- Who steps in when an intrusion is detected? Clearly defined responsibilities, response plans and remediation processes help prevent confusion in an emergency.
- Do you have the required expertise? Maintaining a 24/7 monitoring and response capability requires specialized resources. Depending on your needs, these can come from an in-house team, a managed security services provider or a combination of both.
Security measures must be tailored to your company’s specific circumstances, operations and the potential consequences of an incident. Effective defence relies not only on the technologies in place, but also on the expertise and readiness of the teams in charge of responding.
Is your organization sufficiently prepared to detect and counter a cyberattack? Contact us to have your security measures assessed.