Fraud and Artificial Intelligence: how can you Protect Your Business?
Convincing emails, cloned voices, fake video conferences: artificial intelligence is blurring the reference points we once relied on to detect fraud. How can we better protect ourselves?
Not too long ago, a series of spelling and grammatical errors, awkward wording or an unusual request in an email were often enough to raise suspicion. These are still warning signs, but they can no longer reliably distinguish a legitimate message from a fraud attempt on their own.
Artificial intelligence did not invent phishing or the impersonation of senior executives, suppliers or other trusted contacts. It does, however, make these attacks easier to personalize and carry out on a large scale, giving fraudsters more effective ways to target victims while making their requests seem legitimate.
As a result, fraud is becoming increasingly difficult to recognize.
The warning signs of fraud are harder to spot
Artificial intelligence is making social engineering harder to detect. This technique manipulates people into doing something they would not otherwise do, often by exploiting urgency, trust and emotion.
The principle is not new, but the methods have changed. Information available online allows fraudsters to tailor their approach, imitate a supplier’s usual writing style or refer to an actual situation. By compromising the account of someone the victim knows, the fraudsters can also insert themselves into previous legitimate conversations.
Even employees familiar with phishing now face fraud attempts that are far harder to recognize. And email is just one of the many channels fraudsters use.
When familiar voices and faces become a trap
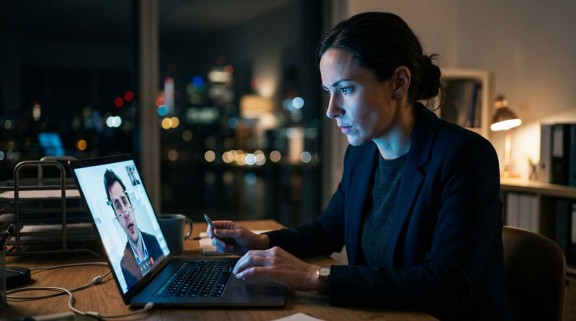
Imagine your company’s CEO calling to ask you to approve an urgent payment. The voice is familiar. Minutes later, the CEO appears in a video conference to confirm the transaction. Everything seems legitimate, yet the person on the other end may not be who you think.
Cloning tools are making scenarios like this increasingly common. Some models can replicate a voice from just a few seconds of audio. For fraudsters, finding a sample is child’s play when an executive speaks at conferences, posts videos or regularly shares audio content on social media.
The deception can extend to identity theft. Sophisticated digital manipulation can reproduce a person’s appearance, gestures and speech patterns, sometimes in real time.
Seeing or hearing someone is therefore no longer enough to verify their identity. An unusual request calls for additional verification through other means.
The real target: the decision-making chain
These new forms of impersonation illustrate the limits of individual vigilance. The most convincing schemes use a series of interactions to make a fraudulent request seem legitimate.
Consider a compromised email account. A fraudster tracks exchanges with a supplier, waits until a transaction is scheduled, then changes the payment instructions. A phone call may follow to confirm the request. From the employee’s perspective, everything checks out: the contact is familiar, the transaction was expected and the call dispels any lingering doubts. Securing the entire financial decision-making chain is therefore essential.
The scale of the problem is significant. According to the Canadian Anti-Fraud Centre, reported spear-phishing losses across Canada totalled 57.7 million dollars in the first six months of 2026, compared with more than 68 million for all of 2025. These schemes often impersonate trusted individuals to redirect payments or change banking details.
In April 2026, a Quebec-based company fell victim to such a scheme. Fraudsters impersonated legitimate contacts and manipulated email correspondence to provide false payment instructions, leading the organization to authorize two transfers. Fortunately, in this case, prompt reporting and a coordinated response by the Canadian Anti-Fraud Centre, financial institutions and investigative partners led to the recovery of approximately 3.5 million dollars.
Double- or triple-checking is time well spent
Since emails, voices and even entire identities can be fabricated, protection against cyberthreats cannot rely solely on an employee’s ability to spot a fake. A few established procedures can help prevent fraud when a request is unusual or sensitive:
- Confirm the request using contact information you already know, not the details provided in the message;
- Make certain transactions subject to a second approval;
- Set up an agreed verification code for certain requests;
- Define a clear process for handling requests to change a supplier’s banking details.
The aim is not to complicate every transaction, but to determine in advance which requests require additional verification and how those checks should be carried out. Establishing such a process is much harder under pressure.
Make awareness a priority
However, such measures are effective only if the people involved are aware of them and remember to apply them.
Awareness training must therefore keep pace with evolving fraud tactics. Training focused solely on suspicious emails may leave employees unprepared for a call that sounds like their manager or another highly convincing impersonation.
Simulations are particularly valuable here. By placing employees in realistic situations, they provide an opportunity to observe responses and tailor training to employees’ responsibilities and the challenges identified.
The goal is not to make every employee a cybersecurity expert. Rather, it is to provide them with clear guidelines: recognizing situations that call for extra caution, properly verifying requests and knowing what to do if doubts persist.
As fraud techniques become increasingly sophisticated, defence mechanisms must also evolve. Well-defined procedures, ongoing awareness training and practical exercises help organizations prepare to respond to a fraud attempt.
Seeking to better prepare your business against new forms of fraud? Contact us!